Banning a single consumer navigation application does not close a sovereign telemetry leak; it merely shifts the routing query to another endpoint while exposing the structural fragility of public-sector mobility governance. When Malaysian authorities restricted civil servants from using Waze during official duties in October 2026, citing data protection and jurisdiction concerns tied to its Israeli origins, the policy landed on a genuine security nerve while leaving core architectural contradictions unresolved. Standard news coverage treats this episode as a straightforward clash between foreign platform risk and domestic cybersecurity. A rigorous operational audit shows something far more intricate: a collision between corporate jurisdiction, aggregate movement intelligence, background operating-system telemetry, and domestic software readiness.
This analysis evaluates the strategic mechanics behind restricting navigation software for public officials, separates verified facts from analytical hypotheses, maps the causal chains that surface-level reporting misses, and outlines an operational governance model for sovereign location data. If you liked this article, you should look at: this related article.
What Is Known Versus What Remains Analytical Inference
Precision starts by separating established public facts from reasoned security hypotheses. Publicly available reporting establishes several concrete facts regarding the October 2026 directive:
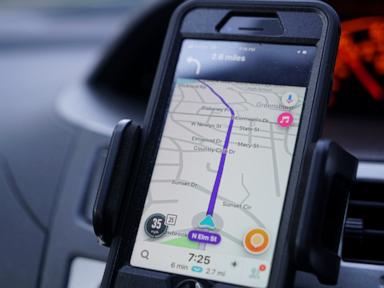
- Prime Minister Anwar Ibrahim ordered an immediate prohibition on civil servants using Waze while carrying out official duties, citing concerns over the protection of government information and personal data.
- National security and cybersecurity officials, including representatives from the National Security Council (MKN) and the National Cyber Security Agency (NACSA), stated that the restriction targets Waze specifically due to legal jurisdiction and Israeli corporate roots, while Google Maps was not covered by the ban.
- Authorities noted that the ban applies to official duties rather than operating as a blanket prohibition on all citizens, though officials urged broader caution and encouraged adoption of domestic alternatives such as TuJu.
- Waze denied that it collects sensitive government information or enables third parties to exploit user data, emphasizing privacy controls and compliance with global data standards.
- Local navigation software such as TuJu experienced sharp download growth alongside user reports of crashes, routing inaccuracies, and missing features during the transition.
Everything beyond those documented facts belongs to analytical inference. There is no public evidence proving active espionage or covert exfiltration of Malaysian official movements via Waze. Security analysts distinguish between capability and exposure on one hand and confirmed malicious exploitation on the other. In intelligence and information security assessments, governments routinely act on structural exposure—such as legal compulsion laws, cross-border data flows, or metadata aggregation—before any breach is publicly demonstrated. Treating exposure as proof of compromise distorts risk scoring, just as dismissing exposure because no breach is proven ignores basic threat modeling. For another look on this story, see the latest update from The Next Web.
The Four Pillars of Sovereign Navigation Risk
Standard commentary tends to flatten app bans into a single question: Can the app spy on the user? In practice, public-sector geolocation risk rests on four distinct pillars that interact dynamically.
Legal Jurisdiction and Compulsion Exposure
Corporate ownership and legal domicile determine which statutory regimes can compel disclosure or shape operational governance. Waze was founded in Israel and acquired by Alphabet's Google in 2013, creating a multi-layered corporate and legal footprint. Officials pointed to Waze's ties to Israeli jurisdiction as a decisive factor distinguishing it from alternatives. From a legal-risk standpoint, a platform operating across multiple jurisdictions faces potential statutory demands, affiliate data sharing, or governance dependencies that may conflict with a state's foreign policy or national security posture. Jurisdiction does not equal automatic compromise, yet it defines the outer boundary of legal recourse for the host government.
Spatiotemporal Metadata and Pattern-of-Life Aggregation
A single coordinate pair—latitude, longitude, and timestamp—carries low operational value on its own. Value emerges through spatiotemporal correlation across cohorts and time windows. When hundreds or thousands of public officials travel along similar corridors, pause at sensitive facilities, or converge on non-public locations prior to policy announcements or security operations, aggregate movement patterns can yield pattern-of-life insights. Even without reading a single classified document, an adversary observing persistent clustering around ministries, diplomatic sites, or infrastructure nodes can infer staffing rhythms, logistics routes, and institutional priorities.
SDK, Background, and Platform-Layer Leakage
Mobile navigation rarely operates as an isolated binary. Modern mapping apps interact with operating-system location services, background processes, crash reporters, analytics libraries, and advertising or telemetry SDKs. Public officials have noted that location exposure can persist even when an application is not actively open in the foreground. Furthermore, mobile operating systems themselves (iOS and Android) mediate hardware GNSS, Wi-Fi scanning, and cell-tower triangulation. Banning one user-facing map client while leaving underlying OS location permissions, third-party SDKs, or alternate mapping apps untouched leaves parallel telemetry channels open.
Domestic Readiness and Operational Continuity
Security controls fail when they ignore human workflow friction. If civil servants are told to stop using a mature routing tool and switch immediately to a domestic alternative that suffers from crashes, map lag, or poor traffic data, two failure modes appear:
- Shadow compliance: Personnel use personal accounts or unapproved devices to get reliable routing on tight schedules.
- Operational degradation: Officials arrive late, take suboptimal routes, or waste cognitive bandwidth fighting buggy software during real-world assignments.
A security policy that degrades field execution without closing upstream telemetry paths produces net operational loss.
Causal Chains Missed by Surface-Level Coverage
Shallow reporting treats the ban as a discrete event: Government dislikes Waze's jurisdiction -> Government bans Waze. Real-world systems behave through second- and third-order causal loops that change the risk profile in unexpected ways.
Asymmetric Platform Substitution
Allowing civil servants to use other commercial navigation apps while banning Waze creates asymmetric platform substitution rather than sovereign isolation. Routing queries, origin-destination pairs, and dwell-time signals simply migrate to whichever mapping service remains permitted or preferred on the device. Unless those permitted services undergo identical technical audits, data-retention limits, and enterprise governance controls, the state has changed the recipient of the telemetry rather than eliminating external visibility into official travel.
Upstream Map-Engine Dependencies
A domestic navigation interface is not automatically a sovereign stack from top to bottom. As officials themselves acknowledged when discussing local alternatives, domestic routing apps can rely on underlying commercial map data or external infrastructure components. When a local app sits atop third-party base maps or cloud services, upstream dependency risk remains. A user-facing rebrand improves domestic product ownership and UI control, yet underlying tile requests, search queries, or infrastructure hosting may still touch external ecosystems unless explicitly architected otherwise.
Incentive Distortion During Emergency and Field Operations
Public administration is not purely desk work. Inspectors, disaster responders, procurement officers, and field administrators operate under time pressure and dynamic road closures. When an approved replacement app lags or crashes during peak traffic, time pressure acts as a strong behavioral catalyst. In organizational security, convenience is a primary driver of policy circumvention. Without frictionless, reliable alternatives—or clear rules separating personal commuting from official dispatch—enforcement relies heavily on post-hoc disciplinary threats rather than preventive architecture.
The Policy Credibility Trade-Off
Singling out one application without publishing transparent technical criteria invites skepticism from civil servants and technical observers alike. If employees perceive a ban as purely symbolic or politically reactive rather than grounded in verifiable engineering standards, compliance drops and policy fatigue rises. Conversely, a risk-based standard applied uniformly across software categories builds institutional credibility because the rule targets data behaviors and legal exposure rather than shifting headlines.
An Operational Governance Framework for Public Mobility
To move from reactive app bans to durable control, public institutions can structure location governance around a four-stage operational sequence. This approach applies established defense-in-depth and zero-trust data principles to government mobility.
- Segment devices and profiles by role. Separate personal devices and personal profiles from managed government devices used on official duties. Do not mix personal leisure routing with official site visits on the same identity token or unmanaged handset.
- Enforce baseline telemetry minimization. Require Mobile Device Management (MDM) policies that restrict background location access to approved tools, disable non-essential ad/analytics SDKs where feasible, and enforce short retention or on-device processing wherever supported.
- Evaluate navigation tools against a unified risk rubric. Score every candidate app—foreign or domestic—on legal jurisdiction, data residency, third-party sub-processors, encryption in transit, and operational reliability before granting official approval.
- Gate rollout on reliability and fallback protocols. Benchmark domestic alternatives under real traffic loads, publish clear guidance on permitted tools and exceptions, and provide sanctioned fallback procedures when primary routing services experience outages.
Limitations and Boundary Conditions of This Framework
No technical or administrative framework eliminates geolocation risk completely. Four structural limitations define the boundary of what this model can achieve:
- Cellular and network-level metadata: Even with app-level restrictions and MDM controls, telecom carriers inherently observe cell-tower handoffs and network routing metadata unless protected through specialized government communication arrangements.
- Commercial hardware and OS ecosystems: Most public-sector fleets run on commercial mobile operating systems whose core telemetry behaviors are governed by global platform vendors rather than individual national agencies.
- Engineering maturity trade-offs: Building and maintaining high-accuracy, real-time crowd-sourced traffic maps requires massive active user density and continuous map curation; small or newly scaled domestic apps face natural accuracy gaps compared to global incumbents.
- Enforcement versus trust: Strict monitoring of civil servants' movements to verify ban compliance creates its own privacy and morale tension within the public service, requiring clear legal boundaries and auditability.
Strategic Recommendation for Sovereign Mobility Policy
Governments and public-sector security leaders should treat the Waze restriction as an inflection point to replace app-by-app bans with a standardized, auditable Software Bill of Data and Jurisdiction for all official mobile tools. Rather than relying on ad-hoc announcements that leave adjacent mapping apps untouched or push stressed staff toward unstable software, agencies should mandate a published risk rubric governing all location-aware applications, pair strict MDM controls on official devices with rapid engineering investment in domestic mapping reliability, and reserve prohibitions for tools that fail objective legal, architectural, or security thresholds.